
TL;DR: VoIP security for professional services firms became a measurable risk in the first half of 2026, with 332 million scanning and cracking attempts recorded against SIP-based phone systems, a scale unique to this sector. That activity sits within a wider surge in attacks against the sector: 3 billion intrusion prevention events and 69.9 million ransomware hits, more than any other industry SonicWall tracks. The underlying cause is structural, phone systems, client portals and collaboration tools built for accessibility, without matching security controls behind them. Firms in the sector should have their current security posture assessed against this specific pattern of attack.
Professional services firms, law firms, accountancies, consultancies and engineering practices, generated more cyber attack traffic in the first half of 2026 than any other sector SonicWall tracks, and a large share of it was aimed squarely at phone systems. VoIP security for professional services firms has moved from a low priority to a measurable risk: 332 million scanning and cracking attempts hit SIP-based phone systems in six months, a scale no other sector saw. That volume sits inside a wider picture of three billion intrusion prevention events and sustained ransomware activity across the sector.
Why the Cyber Security Risks for Professional Services Firms Have Increased
Professional services doesn’t typically generate the same cyber security headlines as healthcare or financial services. The first half of 2026 suggests that’s no longer an accurate picture. Drawing on data from more than one million security sensors, SonicWall recorded three billion intrusion prevention system events against law firms, accountancies, consulting practices and engineering firms between January and June, the largest attack volume of any sector it tracks, not per device, in total.
Four hundred and sixty organisations in the sector were actively detecting ransomware campaigns during the same period, the broadest exposure of any vertical SonicWall monitors. That breadth is the important detail: rather than a small number of high-profile firms absorbing most of the attacks, this is a sustained pattern running across firms of every size, from sole-practitioner consultancies to large regional practices.
Directory traversal attempts, malformed request probes and remote code execution attempts account for 72% of all attack volume in the sector. Old gaps are still being exploited at scale, alongside new ones.
VoIP Security for Professional Services Firms: Why Phone Systems Are a New Entry Point
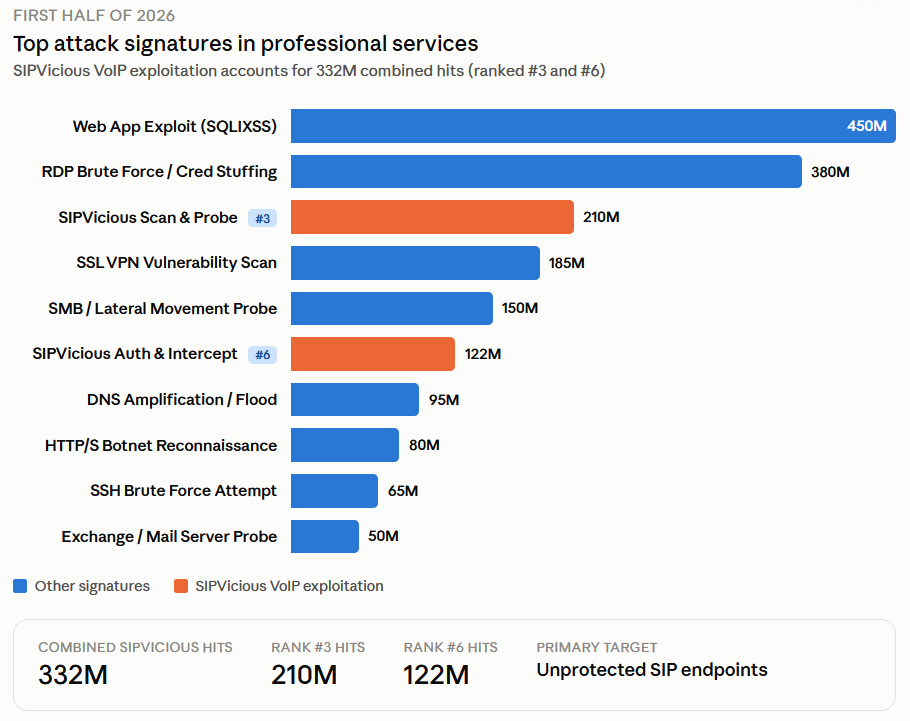
The clearest sign of how targeted this sector has become is a single statistic: 332 million hits from SIPVicious, a scanning and password-cracking tool built for VoIP systems, in the first half of 2026 alone. Professional services is the only sector where this pattern appears at this scale, not just one of several affected industries. That concentration points to a structural weakness specific to how this sector runs its phone systems.
SIPVicious works by scanning wide ranges of internet addresses for phone systems that respond, then testing which extensions can be registered, then attempting to crack the password on those that can. Once an extension is compromised, attackers can route calls to premium-rate numbers at the firm’s expense, a scheme that can run up tens of thousands of pounds in a weekend. Where the phone system shares a network with client portals or document management platforms, a compromised extension can also become a route into those systems.
The reason this concentrates so heavily in professional services is structural. These firms typically run distributed phone infrastructure across multiple offices and remote workers, with endpoints that need to be reachable from outside the network by design. What’s often missing is the authentication enforcement and network segmentation needed to limit what an attacker can reach once they’ve found a way in.
Ransomware Is Targeting What Firms Hold, Not Who They Are
Professional services recorded 69.9 million ransomware hits in the first half of 2026, more than any other industry SonicWall tracks. Ten active ransomware families operated against the sector simultaneously: Filecoder alone generated 19.1 million hits across 113 organisations, alongside 11.9 million from Gandcrab and 10.5 million from Ryuk. Ten families running simultaneously against 460 organisations reflects a coordinated, sector-wide campaign rather than a handful of opportunistic hits.
Some of these families are not new. Gandcrab first appeared several years ago, yet it still generated close to 12 million hits against this sector in six months. That persistence says as much about unpatched, unmonitored systems still in production as it does about the ransomware itself.
Client records tied to live legal or financial matters carry a kind of leverage that ordinary personal data doesn’t, and privileged correspondence adds another layer on top of it. Ransomware groups understand that leverage translates directly into a firm’s willingness to pay, to avoid disclosure or downtime. The sector’s ransomware exposure reflects a calculated assessment of what these firms are likely to do under pressure, not a random targeting pattern.
What This Means in Practice
This data doesn’t point to a single fix so much as a pattern: a weak point in one system, a phone extension, a portal login, an unpatched server, rarely stays contained to that system alone. The interconnected way these platforms are typically built is exactly what makes a single compromise expensive.
For firms in this sector, the practical question isn’t whether an attack will be attempted, the data suggests it already has been. The question is whether the firm’s current setup, its phone system, its client-facing portals, its network segmentation, has kept pace with how specifically this sector is now being targeted. Many haven’t had reason to ask that question until now.
That gap is rarely visible until it’s tested, which is exactly what the attackers in this data set are doing at scale. Waiting for an incident to reveal it is the expensive way to find out.
Concerned? We can help
This data is best treated as a prompt to check where the gaps actually sit, rather than cause for alarm. A security posture audit gives professional services firms a clear, evidenced picture of where their phone systems, network access and client-facing platforms currently stand against exactly this kind of targeting.
Marlin Communications carries out these audits across the sector. Get in touch if you’d like to arrange one for your firm.
About Marlin Communications
Marlin Communications is an independent, single-source provider of business communications & collaboration solutions including voice, data, mobile, video, network security and contact centre technology for businesses of 50 – 5,000 staff.
We operate throughout the UK – with global reach – and our own, on-premises, 1,000 ft² Technology Suite at our Bath office, where we host regular events and showcase technology solutions for our clients. Contact us for your free comms audit or product demo.
Marlin Communications is ISO 27001 certified by BSI under certificate number IS795313.
Get the latest tech news & reviews – straight to your inbox
Sign up to receive exclusive business communications, tech content, new tech launches, tips, articles and more.
Click here to follow our LinkedIn company page and stay up-to-date with our LinkedIn newsletter